8 eMudhra digital certificates compromised; private keys leaked due to weak code..
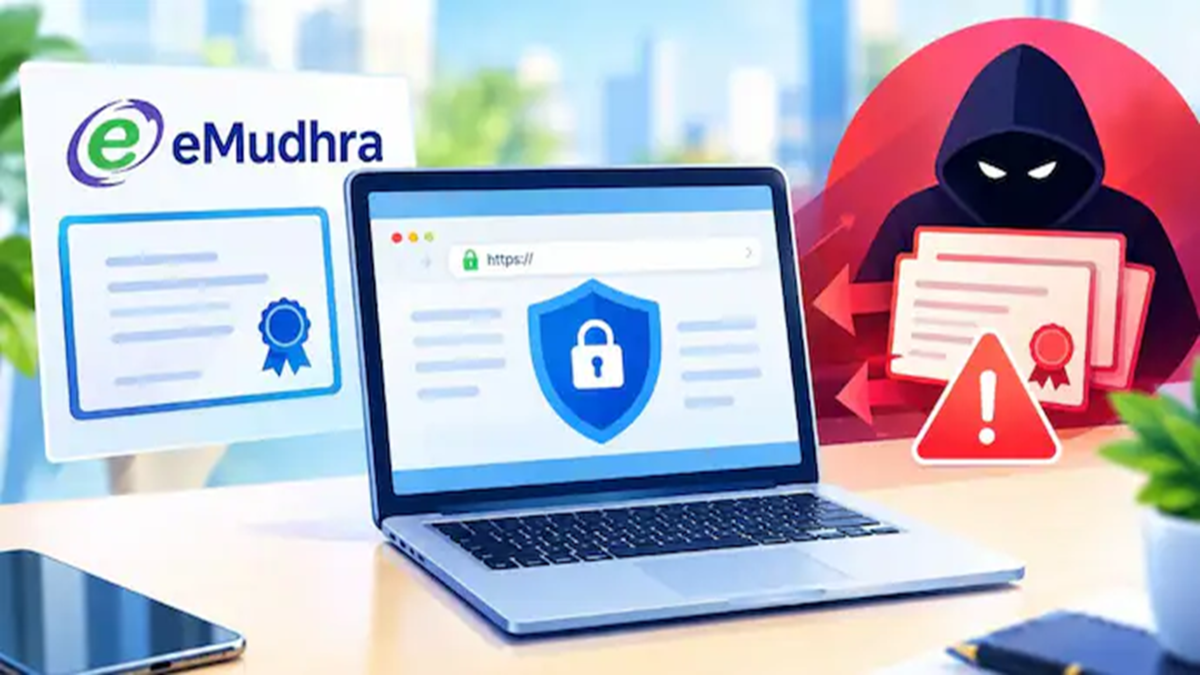
The private cryptographic keys for eight critical intermediate certificates belonging to eMudhra—a major Indian certification authority—have been compromised. On October 21, 2026, the Indian Computer Emergency Response Team (CERT-In), the government’s cybersecurity agency, issued an advisory regarding this incident. The root cause of this technical lapse was weak coding—specifically, insufficient cryptographic randomness—which led to the exposure and insecurity of highly sensitive digital keys.
The compromised keys included six TLS (Transport Layer Security) certificates and two code-signing certificates. In simpler terms, these digital keys serve as legal proof of the authenticity of websites or software on the internet. Had they fallen into the wrong hands, cyberattackers could have forged digital certificates, masquerading as banks, government portals, or corporations. This would have enabled the creation of deceptive, authentic-looking websites, allowing attackers to easily steal sensitive login credentials and financial data from internet users.
What is eMudhra, and why is its role significant?
eMudhra is a licensed certifying authority that serves as a cornerstone for digital identity and internet security in India. Its Digital Signature Certificates (DSC) and 'eSign' services are used for signing income tax returns, government e-tenders, and corporate documents. Furthermore, it plays a pivotal role in issuing SSL/TLS certificates, which secure data transmitted between websites and internet servers.
No direct attack on end-users
Despite the severity of this threat, the security lapse was fortunately detected in time. According to CERT-In, eMudhra has clarified that no end-user certificates were issued to general customers or users from the affected intermediate certificates. Google has also confirmed that there was no evidence of misuse or any suspicious activity involving these six TLS certificates prior to their being blocked.
Major Action by Google and Mozilla
Given the seriousness of the matter, global tech companies have taken immediate and stringent action. Mozilla has blocked the affected TLS certificates and released new security updates for the Firefox browser. Meanwhile, Google has implemented stricter security filters in the Chrome browser and has initiated the process of removing eMudhra’s ‘emSign ECC Root CA – G3’ root certificate from its root store.
What Should Users and Companies Do?
To address this cyber threat, the government agency CERT-In has issued essential guidelines for both internet users and system administrators:
Immediately update your Firefox browser, Chrome browser, operating systems, and all other critical software to their latest versions.
Verify the validity and status of the digital certificates currently in use across your systems and websites.
Remove any affected certificates immediately and replace them with new ones from a fully secure and trusted authority.
Do not ignore any ‘Security Warning’ or ‘Not Secure’ alerts that appear on your screen while browsing the internet.
Keep a close watch for any suspicious changes or unauthorized activity within website files and software code.
Disclaimer: This content has been sourced and edited from News18 Hindi. While we have made modifications for clarity and presentation, the original content belongs to its respective authors and website. We do not claim ownership of the content.