Google's major revelation: Dangerous zero-click bug found in Pixel smartphones—how was data being stolen without even touching the phone?
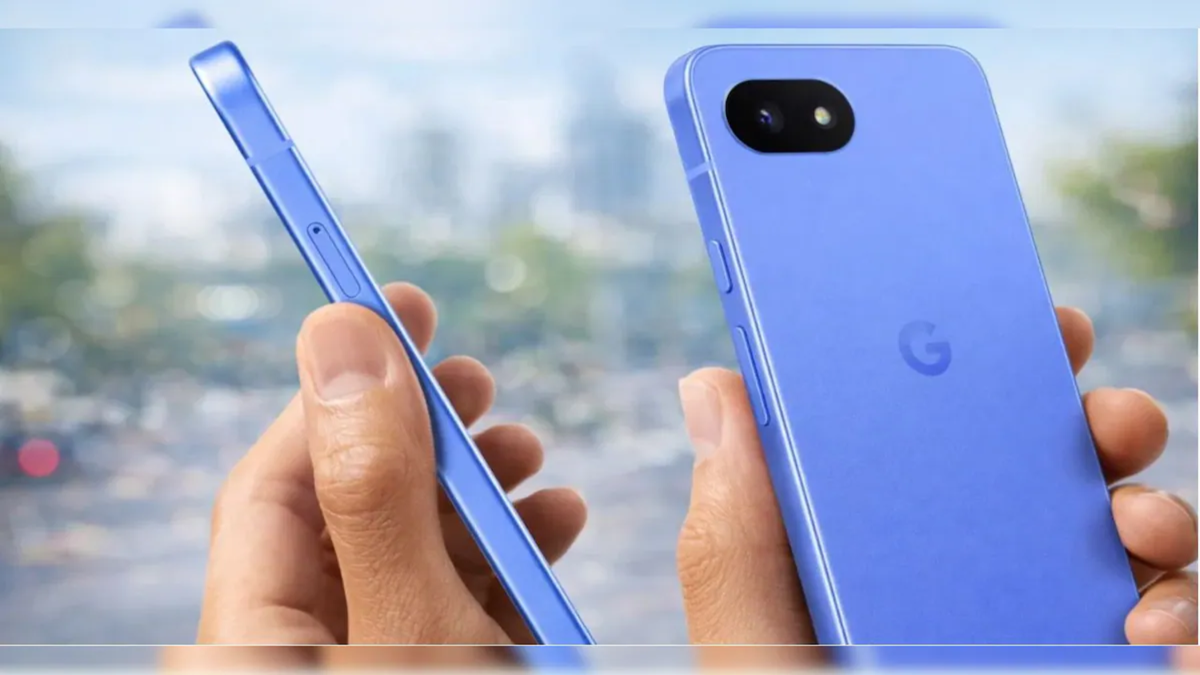
Google has officially confirmed that limited, targeted cyberattacks exploited a critical software bug in its Pixel smartphones. This vulnerability is being tracked as CVE-2026-58704. However, Google has since patched the bug.
**What was the vulnerability in the smartphone?**
According to available information, the security flaw existed in the Pixel phone's modem—the key component that connects the device to mobile networks and the internet.
By exploiting this vulnerability, attackers could bypass the security boundaries of the modem's sandbox. This could potentially grant them access to the phone's broader data and system. Such a flaw is classified as a "privilege escalation" vulnerability, meaning it allows an attacker to gain system access beyond their initial, limited permissions.
**How dangerous was this cyberattack?**
The most alarming aspect of this bug was that it could be used to launch a "zero-click" attack. Exploiting it required no interaction from the phone's owner; the user did not need to click a suspicious link, open a file, or install an app—actions that might otherwise have raised an alarm.
This type of exploit is known as a zero-click attack, where an attacker leverages a specific system or software vulnerability to compromise a device without any active participation from the victim.
**Who carried out the attack?**
Google has not yet disclosed the identity of the attackers or the group behind the exploitation of CVE-2026-58704. A company spokesperson did not respond to a request for comment on the matter.
However, such security vulnerabilities are often exploited by surveillance vendors. These companies develop software for monitoring and data extraction, and in many instances, their technology is sold to governments or law enforcement agencies. However, based on available information, the involvement of any specific company or group behind this particular Pixel bug has not been confirmed. Google has also not disclosed who exploited the vulnerability.
Google Releases Patch
The company states that CVE-2026-58704 has now been patched. This incident highlights that security vulnerabilities in hardware-related software within smartphones—such as modems—can also serve as entry points for cyberattacks.
Advice for Users
Experts advise that if you use a Google Pixel smartphone, you should first go to your phone's settings, navigate to 'System' and then 'System Update,' and download and install the security update to ensure your phone is fully secure.
Disclaimer: This content has been sourced and edited from Amar Ujala. While we modified it for clarity and presentation, the original content belongs to its respective authors and website. We do not claim ownership of the content.